AI is now part of the attackers’ arsenal in Latin America Artificial Intelligence is no longer just a tool for improving productivity, automating tasks, or assisting cybersecurity teams. Threat actors
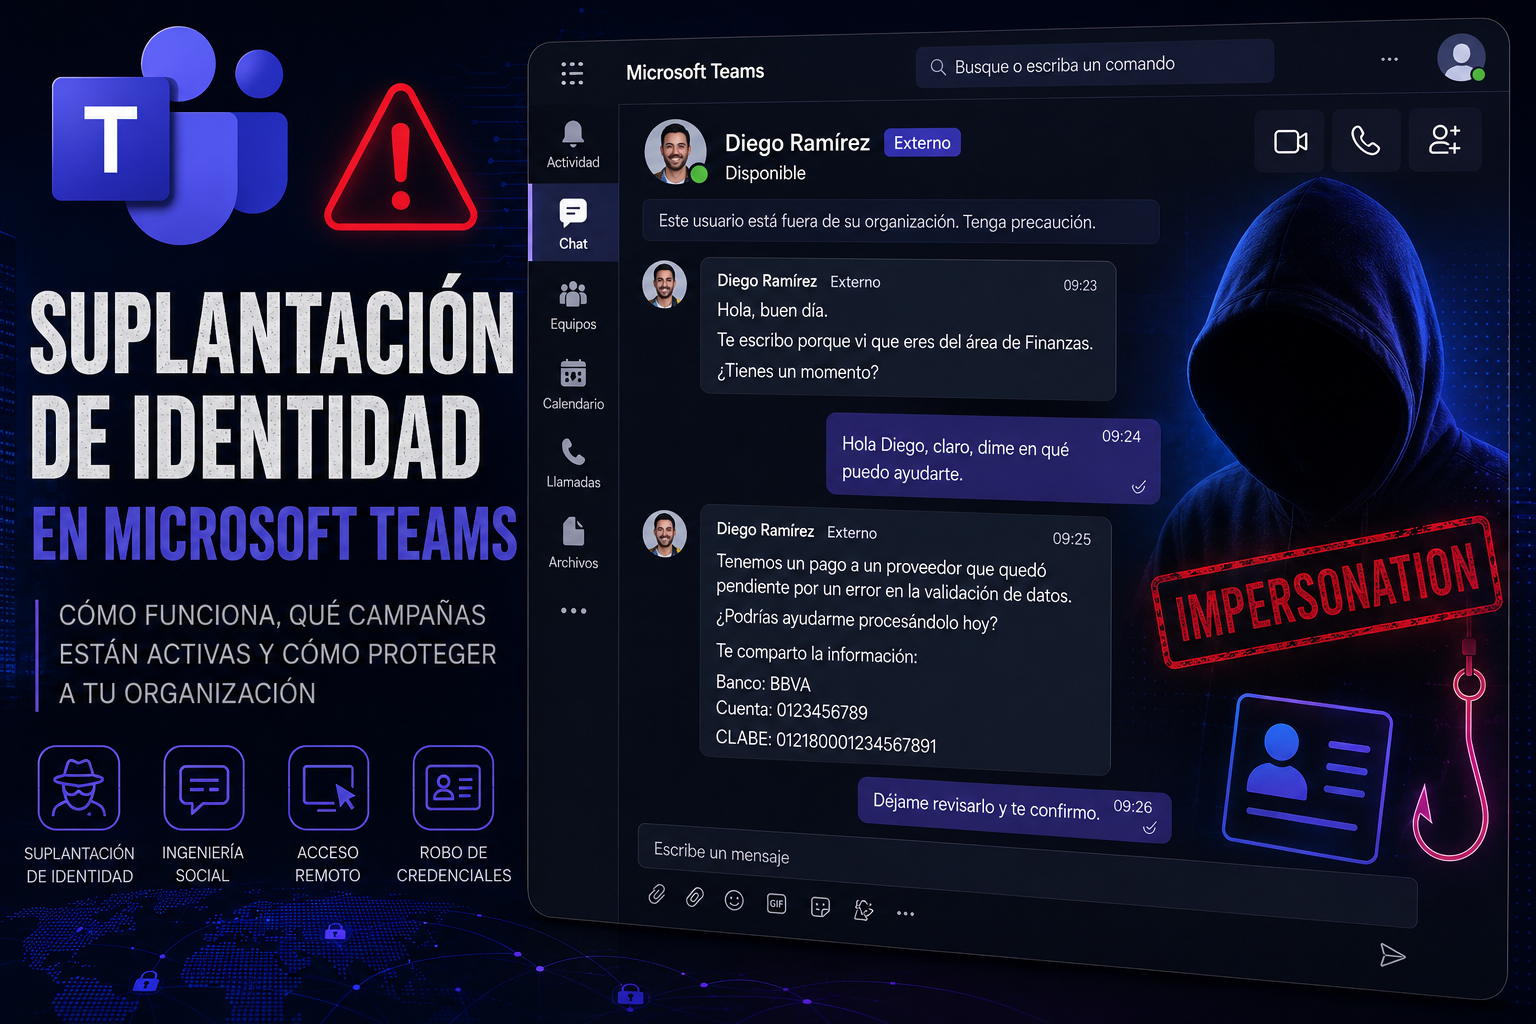
For years, email was the primary channel used by cybercriminals to execute phishing campaigns. However, the increase in hybrid work and the massive adoption of collaboration platforms such as Microsoft
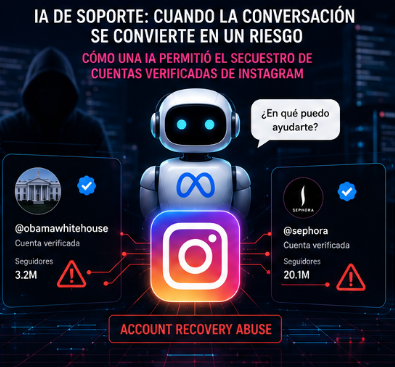
For years, major tech platforms have promoted AI-powered automation as a way to reduce costs, speed up processes, and improve the user experience. However, an incident recently confirmed by Meta
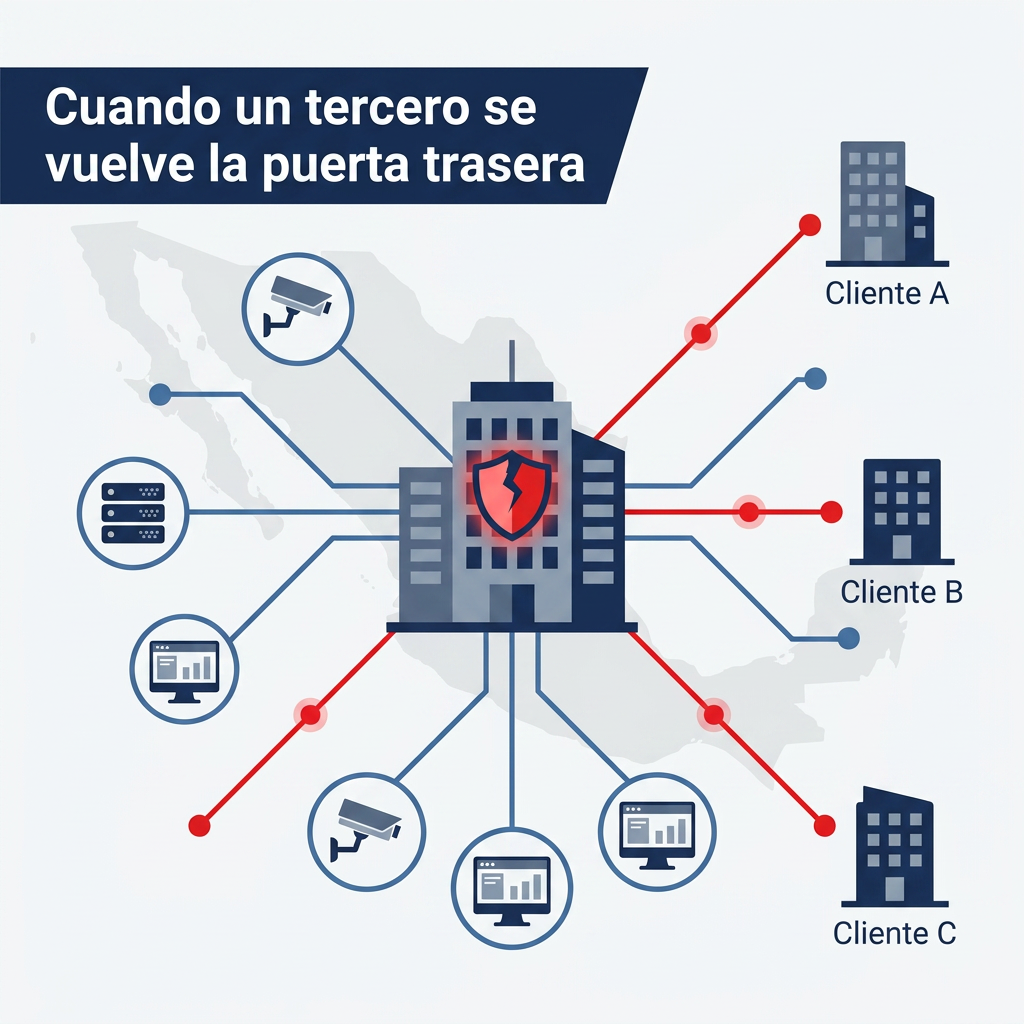
The same old story In 2026, the incident that affected a cybersecurity services provider a security services provider in Mexico once again delivered an uncomfortable but necessary lesson: a provider’s
A supply chain attack campaign named Mini Shai-Hulud was recently reported. It is a worm-type malware that has compromised multiple npm packages, starting with the @tanstack/* ecosystem, publishing malicious versions
Origin and context: The Gentlemen is a cybercrime group specialized in ransomware that emerged in July 2025. Despite its recent appearance, the group demonstrated from the outset a level of
This case study describes a ransomware intrusion affecting an organization operating a hybrid IT/OT environment, where business systems were tightly coupled with operational processes. The attacker, later attributed to Lynx
A recent proof of concept called EDR-Freeze demonstrates how an attacker can put EDR or antivirus processes into a “coma” using legitimate Windows components, without the need for vulnerable drivers
Una operación de takedown se llevó acabó para desarticular la infraestructura utilizada por el ladrón de malware llamado Lumma, dicha operación fue liderada por la Unidad de Delitos Digitales (DCU)
Descubrimiento El equipo de investigación de amenazas ha identificado un nuevo ataque a la cadena de suministro (Supply Chain Attack) que afecta a desarrolladores de bots para Telegram. Se trata
La situación de ciberseguridad en México presenta importantes desafíos debido al crecimiento digital del país y la limitada infraestructura de seguridad. El país ha experimentado un aumento en la actividad
En el cambiante panorama de la ciberdelincuencia, ciertos grupos surgen como amenazas importantes para la seguridad global. Una de esas entidades, Ransomhub, ha ido escalando posiciones hasta convertirse en un
It is with great excitement that we share with you that BeaconLab, the Cybolt threat observatory, and its team specialized in the investigation, detection, analysis, mitigation and response to cybersecurity
Recently Beacon Lab has conducted an investigation of an incident, in which a new ransomware group, named Red Ransomware Group according to their public blog, or also Red CryptoApp (because
In recent years, cybersecurity has become a vitally important issue for governments, organizations and individual users alike, with a huge impact not only globally, but also specifically in Mexico. The
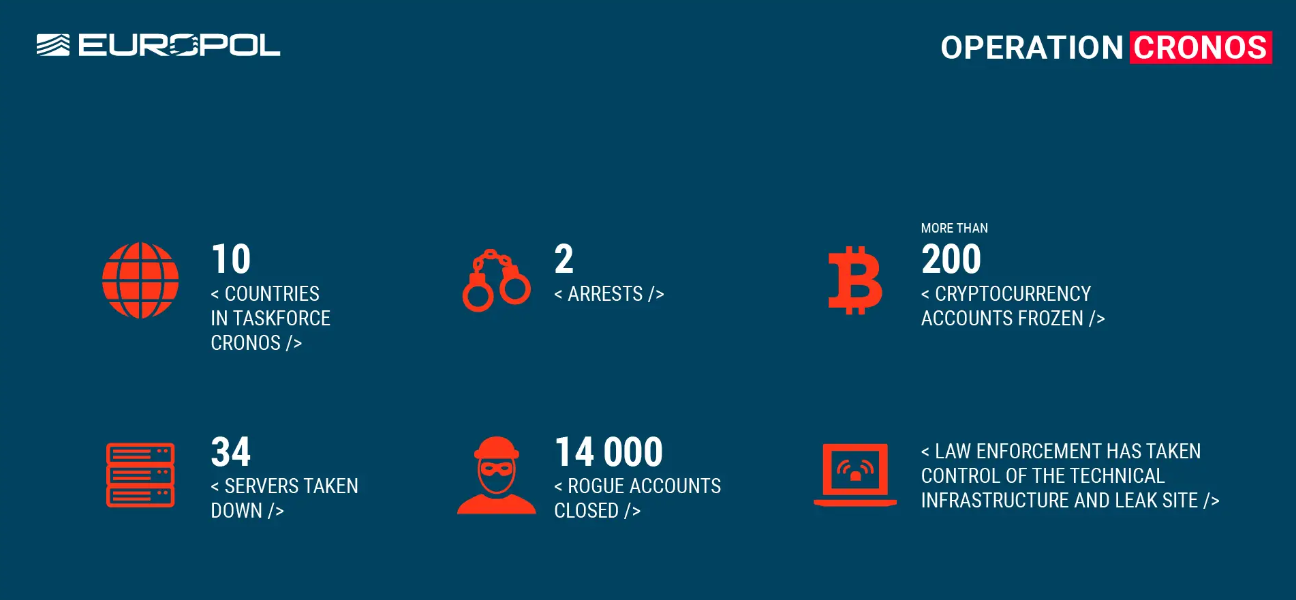
Yesterday, an international operation coordinated between government agencies from the United States, Great Britain, Europol and allies from 10 countries was carried out, which allowed taking down an important part
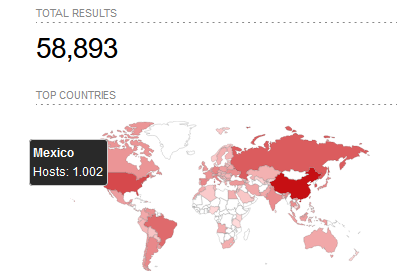
In October 2023 a TrendMicro researcher had discovered and published details of a critical vulnerability in VMware, specifically, in VMware vSphere. This is a management platform for VMware environments, used
Today, cyber threats know no borders. Mexico, like any other country, is exposed to various threats and adversaries, from cybercriminals, hacktivists, insider threats, cyber espionage, and many others. These adversaries
Ransomware is currently one of the most frequent and, above all, one of the most impactful threats for companies around the world, including Mexico. It affects companies of all types