BY CYBOLT

Threat observatory and incident
 response

We protect your company’s infrastructure and digital assets by effectively detecting, resolving, and mitigating cybersecurity incidents

What is a CSIRT?

We protect your company against cyber threats

At the heart of our approach is the operation of a CSIRT. This specialized team is dedicated to the investigation, detection, analysis, mitigation, and response to cybersecurity incidents. We work tirelessly to protect  organizations against cyber threats and collaborate in their post-incident recovery process.

At BeaconLab, we are committed to providing support, collaboration, and guidance during a security incident while also offering recommendations to prevent it from recurring.  We use state-of-the-art research processes and current technologies to protect your digital assets.

If you have any questions or need cybersecurity assistance, do not hesitate to contact our team.

Managing a cyber incident

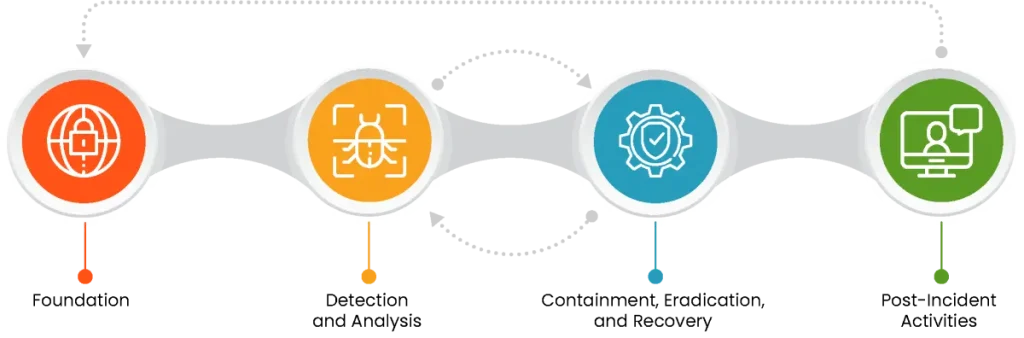
At BeaconLab, we follow the NIST incident response framework, which consists of four key phases. During the preparation phase, response plans are developed, a dedicated team is assigned, and security measures are implemented. During the detection and analysis phase, systems and networks are monitored, and the nature and scope of the incident are thoroughly investigated. The containment, eradication and recovery phase focuses on taking decisive measures to contain and eliminate the incident, as well as restoring normal operations. Finally, in the post-incident activities phase, the incident is reviewed, the actions taken are documented, and improvements are implemented to prevent future incidents.

In addition to following this standard incident management framework, BeaconLab is an active member of FIRST, complying with its guidelines and actively collaborating with the global CSIRT community.

Latest Alerts

Logo de PostgreSQL

Affected product(s):  Product Affected versions PostgreSQL 18 Earlier than 18.7 (includes CVE-2026-116322, unique to this branch) PostgreSQL 17 Earlier than 17.12 PostgreSQL 16 Earlier than 16.16 PostgreSQL 15 Earlier than

Logo de Trend Micro

Affected product(s):  Product Affected versions Apex One (on-premises server, 2019 SP1) Affected; Critical Patch B20113 (PHP module 8.2.35). According to the vendor, it can be installed on SP1 build 11092

Logo de Microsoft

Affected product(s):  Product Affected versions Fixed in Microsoft 365 Apps for Enterprise (32- and 64-bit) Earlier than the November update for the channel in use The November update for each

Logo de PostgreSQL

Affected product(s):  Product Affected versions PostgreSQL 18 Earlier than 18.7 (includes CVE-2026-116322, unique to this branch) PostgreSQL 17 Earlier than 17.12 PostgreSQL 16 Earlier than 16.16 PostgreSQL 15 Earlier than

Logo de Trend Micro

Affected product(s):  Product Affected versions Apex One (on-premises server, 2019 SP1) Affected; Critical Patch B20113 (PHP module 8.2.35). According to the vendor, it can be installed on SP1 build 11092

Logo de Microsoft

Affected product(s):  Product Affected versions Fixed in Microsoft 365 Apps for Enterprise (32- and 64-bit) Earlier than the November update for the channel in use The November update for each